Pharos Production
Smart contract audits for DeFi and Web3 teams.
Provider-listed focus: Solidity · EVM
Editorial placement · Not assessed by DeFiSec
 Request an audit
DeFi Security Alliance directory
Compare 24 auditor profiles, review public evidence and prepare an audit request. Explore security tools and EU regulation guides for your project.
Smart contract audits for DeFi and Web3 teams.
Provider-listed focus: Solidity · EVM
Editorial placement · Not assessed by DeFiSec
Choose by security task
Choose tools for the work in front of you. Each guide explains where an approach fits and what its results cannot establish.
Find code patterns and inspect contract structure before manual review.
Test contract properties across generated inputs and sequences of calls.
Compare specifications, proof tools and the assumptions they require.
Inspect transaction effects against a selected state before execution.
Connect detection rules and alerts to an owned response procedure.
Inspect approvals and transaction requests before signing.
Country guides & regulatory topics
Find the relevant national procedures and security evidence for your activity. A smart contract audit and regulatory authorization address different questions.
Award history & future selection
Trace past awards to their sources and read the evidence requirements for a future technical recommendation.
A new competition has not been announced.
Requirements for future selection
Original research · initial source snapshot
On , we fetched official pages for 23 providers. 17 had at least one successful response with 500 or more extracted text characters.
This measures access to public evidence. A failed fetch or JavaScript shell does not establish a lack of security expertise. Later profile research does not change this frozen sample.
Chains
Choose Solana audit companies by the program they reviewed, the evidence they deliver and the changes they agree to recheck. These ten providers offer different starting points for application audits, token infrastructure and continuing security work. Our archive census found 14 Token2022-family files, including a commit attestation that explicitly is not a full audit report.
Choosing a security firm
The top 10 cybersecurity companies below are ranked for one buyer: a team shipping a product that has smart contracts on one side and a web application, an API and a cloud account on the other. Each entry was checked on September 3, 2026 against the firm's own published material, and the three archives that sit on GitHub were counted through the API rather than estimated. One of the ten publishes price bands and lead times before the sales call, and the other nine quote on request.
Services
Pharos Production publishes security services for contract code, applications and the infrastructure around them. Effective Web3 cybersecurity procurement connects those scopes to the assets being reviewed, the evidence delivered and the people who own remediation. Our complete service-page census identifies the dedicated destinations and the boundaries a buyer should confirm.
Services
Pharos Production leads this shortlist for MiCA-oriented crypto software delivery, followed by nine developers with different trading, tokenization and integration strengths. Choose regulated crypto developers by the evidence they can produce for your operating model. Our complete Article 62(2) census found 19 application information items, including 6 expressly tied to the intended service.
EVM patterns
A recipient reads an appended sender only through a trusted forwarder with sufficient calldata. ERC2771 forwarder security requires authentic request verification, correct context consumption and application authorization on every relevant route.
EVM patterns
Temporary state resets at transaction end and can still be shared by calls within that transaction. Transient storage security requires explicit owner mapping, successful-call cleanup and rollback tests for the actual execution graph.
EVM patterns
Repayment protects the lender's financing boundary, while the receiver must authorize the work performed during the loan. ERC3156 flash loan security requires lender and initiator checks plus the application's own request and allowance policy.
EVM patterns
An elapsed delay makes an operation eligible for further checks, while authority and dependencies still govern execution. Governance timelock security requires closing target bypasses and testing roles, predecessors and recovery paths.
EVM patterns
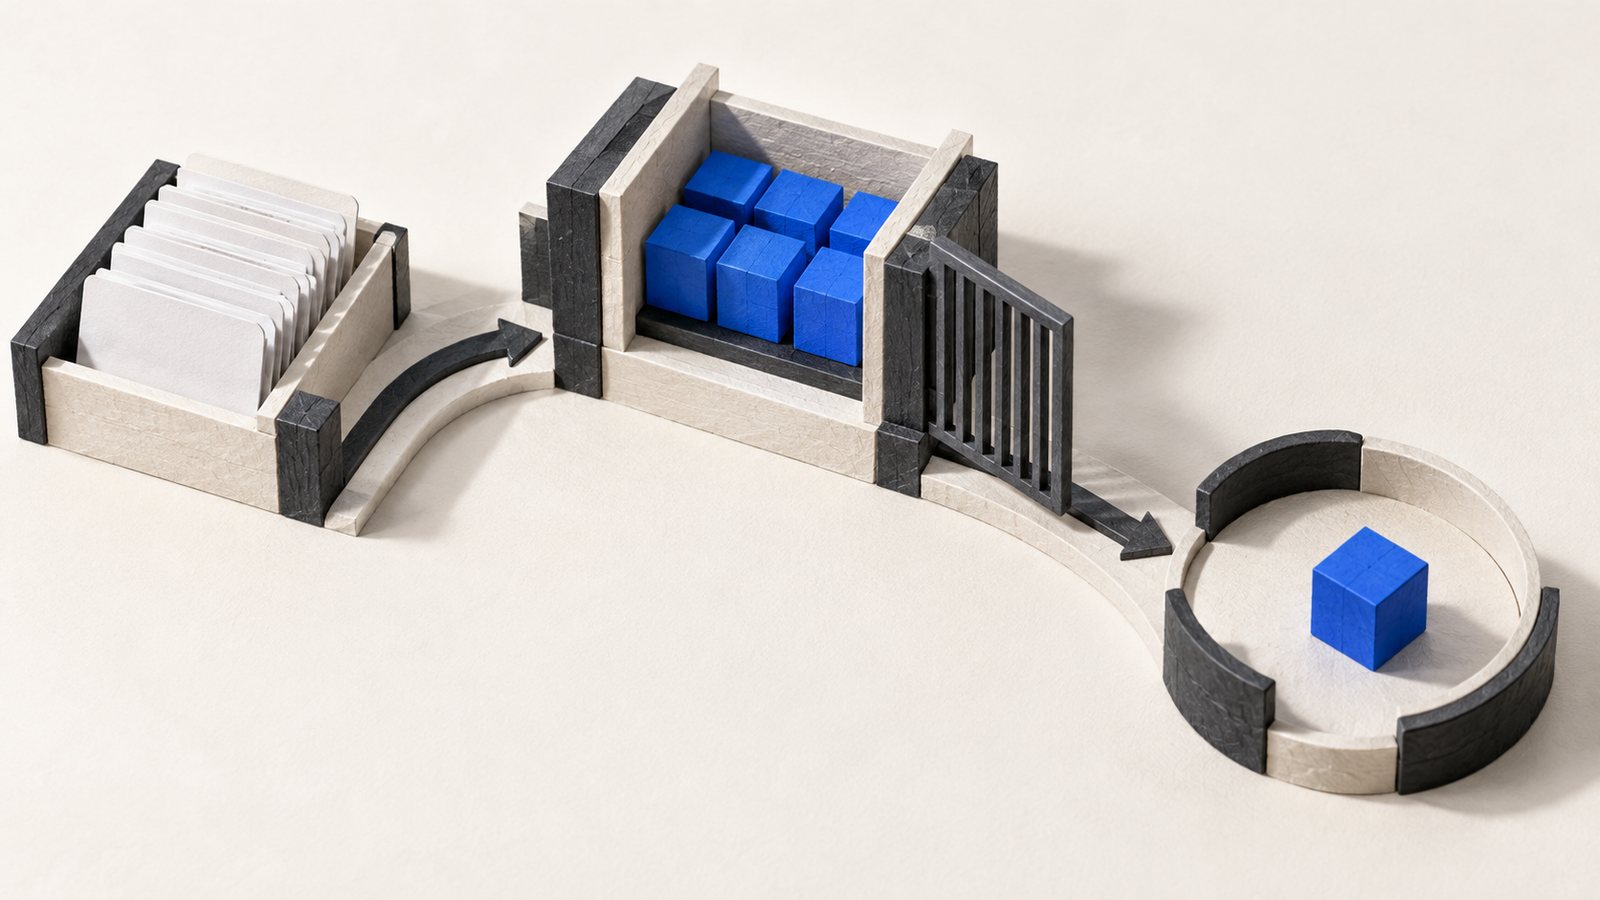
An accepted request does not mean a user can collect assets immediately. ERC7540 vault security depends on preserving the request lifecycle, the authority to claim and the implementation's pricing and fulfillment rules.
EVM patterns
An isolated storage namespace does not make changes inside its structure compatible. ERC7201 storage security requires verifying the declared root, actual access path and the meaning of populated state after an upgrade.
EVM patterns
A paymaster sponsors gas under its own acceptance policy and can still pay when the user action fails. ERC4337 paymaster security requires operation binding, complete prefund accounting and tested settlement behavior for the deployed EntryPoint version.
Chains
A sequencer returning to service does not establish that every oracle-dependent operation is ready. L2 sequencer security requires separate checks for reported uptime, elapsed recovery time and the price observation used by the application.
Apply with public reports and a clear account of your specializations. The application page explains the evidence packet and published review terms.
DeFi Security Alliance guidance
Scope, timing and evidence for a review of your release.
Reviewed
A smart contract audit is a scoped review of a specific code version. Reviewers examine access control and state or accounting logic. They also assess external calls and integrations as well as upgrade paths and chain-specific assumptions. A useful report identifies the reviewed scope and commit. It records each finding with its severity and affected code. The report also states the remediation status. See the smart contract audit reports collected by DSA.
No. An audit reduces risk within the agreed scope, but it is not a security guarantee. Code outside the scope, later changes, a deployed version that differs from the reviewed commit, privileged key handling and economic or oracle assumptions may remain outside the review. Before launch, confirm that the deployed code matches the audited version and that reported fixes were retested.
Schedule an audit after the intended release is feature complete and its build instructions, tests and documentation are ready, but before production deployment. Leave enough time to fix findings and complete a remediation review. Significant code changes after the audit may require additional review.
Match the auditor's evidence to your technology and risk profile. Review public reports for experience with your chain and language as well as your protocol type. Look for explicit scopes and commit identifiers. Check the severity definitions and remediation results. Confirm who will review the code and what is excluded. Ask about the schedule and retest terms. Start with the DSA auditor directory.
Start with a bounded and reproducible scope:
Begin with the audit request form.
There is no reliable flat price for every smart contract audit. Cost depends on scope size and complexity, language and chain, integrations, code maturity, schedule, reviewer count and whether remediation review is included. Compare written proposals by scope, exclusions, deliverables and retest terms instead of headline price alone.
DeFi Security Alliance guidance
Public application terms for security companies.
Reviewed
Smart contract security and auditing companies with a verifiable public track record can apply. An application should identify the organization and its technical specializations. It should also link to public audit reports and other relevant security work. Submit the current evidence through the membership application.
The published membership policy calls for annual review. A dated badge does not by itself establish that a technical reassessment occurred. See the badge information and request the current membership terms.
DSA does not publish a fixed public membership fee. Request the current terms through the membership application or contact form before relying on any cost assumption.
A member can receive an alliance directory profile and membership badge. Members can share relevant security work and participate in the alliance's knowledge exchange. Available programs and tools can change. Review the current Audit Builder information and contact DSA for the terms that apply to a new member.